Enterprise security teams have shifted how they think about integration platforms. A decade ago, a platform like Sterling B2B Integrator was reviewed for uptime and throughput. Today it sits on the same risk register as the firewall and the identity provider, because every partner transaction and every regulated document pass through it.
That shift shows up in how mature organizations operate: continuous vendor patch cycles instead of annual upgrades, platform currency tied to cyber insurance renewals, and cryptographic standards checked with integration vendors every audit cycle. The latest Sterling Integrator algorithm changes are exactly the kind of update this discipline exists to catch.
Why fixpacks break generic CI/CD assumptions
IBM Sterling B2B Integrator sits at the center of how an enterprise exchanges data with suppliers, customers, carriers, and financial partners. Because it works quietly in the background, updates to it are easy to overlook in favor of work that is more visible to the business.
That is exactly why this update deserves attention now. A weakened cryptographic standard inside an integration platform does not stay contained – it travels through every partner connection and every downstream process that depends on the integrity of what the platform delivers.
Legacy Profile | Current Profile |
3DES for encryption | AES for encryption |
SHA-1 for integrity hashing | SHA-256 for integrity hashing |
The Invisible Layer That Keeps Every Transaction Trustworthy
Behind every file exchange, a quiet verification step confirms the document arriving from a partner is exactly the document that was sent, with nothing altered along the way. Both older methods have been shown to fall short of what enterprise data protection now requires.
For a long stretch, Sterling B2B Integrator paired 3DES encryption with SHA-1 hashing. Recent releases have replaced that pair with AES and SHA-256. The shift maps to specific product versions:
| SI Version | Encryption | Hashing |
| Up to 6.2.0.x | 3DES | SHA-1 |
| 6.2.1.x | AES | SHA-1 |
| 6.2.2.x and above | AES | SHA-256 |
Why this matters to the business, not just the integration team:
- Partner trust and onboarding. Larger trading partners increasingly require the AES/SHA-256 standard as a condition of connection. Staying on the older pair can mean failed partner security questionnaires or delayed onboarding.
- Audit and compliance readiness. When a regulator or auditor asks how data integrity is verified across partner exchanges, “3DES and SHA-1” is no longer an acceptable answer in most compliance frameworks.
- Operational continuity. An SI upgrade to 6.2.2.x or later, made without a matching update on the integration side, doesn’t fail gracefully – it leaves PCM unable to connect to SI, exactly when production traffic depends on it.
The Business Case for Upgrading Now
Every day this wait is a day the exposure compounds. A weakened algorithm pair does not announce itself. It sits quietly in production until something exposes it – an SI upgrade that suddenly leaves PCM unable to connect, a partner audit that flags the outdated pair, or an attacker who finds it first. By then, the cost is no longer measured in upgrade hours. It is measured in a stalled trading connection, a failed audit finding, or worse, and the uncomfortable conversation that follows.
It is tempting to treat this as routine IT maintenance. It is not. An outdated algorithm profile is a standing liability, and the clock on it is already running:
- The risk is already accruing. Every day the legacy pair remains active is a day of exposure on the books, whether it has been exploited yet.
- The choice will not stay in your hands. Trading partners and networks are progressively deprecating legacy algorithm support. Waiting only removes control over when the migration happens.
- Waiting is the more expensive option. A planned upgrade, tested on your own timeline, costs a fraction of an emergency migration forced by a live disruption.
The organizations that move first are not reacting to fear. They are protecting something specific: the trust their partners and customers place in every transaction that flows through their systems.
Where PCM Fits into the Picture
A platform update strengthens the standard. PCM is what keeps every connected environment aligned to it without manual intervention each time Sterling Integrator changes underneath it.
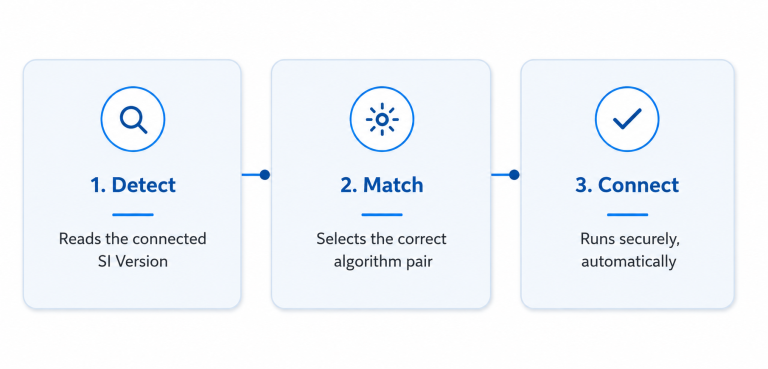
PCM checks the connected SI version the moment it starts up and switches to the matching encryption and hashing profile automatically – nothing to reconfigure, no downtime to schedule.
PCM’s Detect → Match → Connect Process
Environments on SI 6.2.1.x or earlier remain compatible today, running on the legacy profile. The inflection point is SI 6.2.2.x and above: unlocking the AES/SHA-256 profile requires PCM itself to be upgraded to the minimum version for that branch. Without that upgrade, PCM cannot connect to SI on the newer profile — the exact mismatch this advisory exists to prevent.
Even where compatibility holds today, PragmaEdge recommends upgrading proactively rather than waiting for that inflection point to arrive unannounced.
Recommendation. For any environment running Sterling B2B Integrator 6.2.1.0 or later, PragmaEdge recommends upgrading PCM to the latest compatible version now, to stay aligned with current encryption standards. For help planning that upgrade, PragmaEdge’s support team is available atsales@pragmaedge.com
The Outcome That Matters
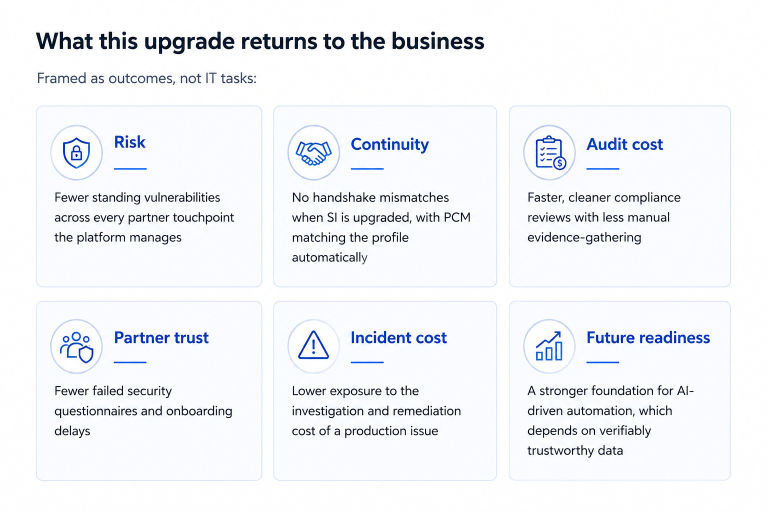
Set aside the version numbers for a moment. What this upgrade actually returns to the business is measurable, and it shows up in places the CFO and the CISO both watch.Even where compatibility holds today, PragmaEdge recommends upgrading proactively rather than waiting for that inflection point to arrive unannounced.
For organizations running Sterling B2B Integrator, the question is not whether this upgrade happens. It is whether it happens on your timeline, or on someone else’s.
Why Enterprises Bring This Work to PragmaEdge
A security upgrade on a platform this central is not something an organization hands to a generalist. PragmaEdge is built specifically around the IBM integration and Maximo Application Suite ecosystem, which is why the version thresholds and recommendations in this piece come from PragmaEdge’s own compatibility advisory, not a general product brief.
- IBM Gold Business Partner – Verified partner status
- Sterling & Integration Focus – Sterling B2B, TIBCO, webMethods, Camunda
- Practice-Led Delivery – Guidance from active engagements, not templates
The deciding factor in an upgrade like this is rarely capability alone. It is whether the partner has done this specific work, on this specific platform, enough times to know where it tends to go wrong before it does. That is the experiencePragmaEdgebrings to the table, offered here as a starting conversation rather than a sales pitch.
Confirm your compatibility before your next SI upgrade